Ideas for the decisions ahead.
Practical perspective on security, technology, and operations — from the team that runs them.
Your Access List Is a Museum. Time to Clean It Out.
An access review needs more than a list of active employees. Supplier accounts, service identities, inherited permissions, and active sessions can preserve access after the original reason has ended.
3 min read →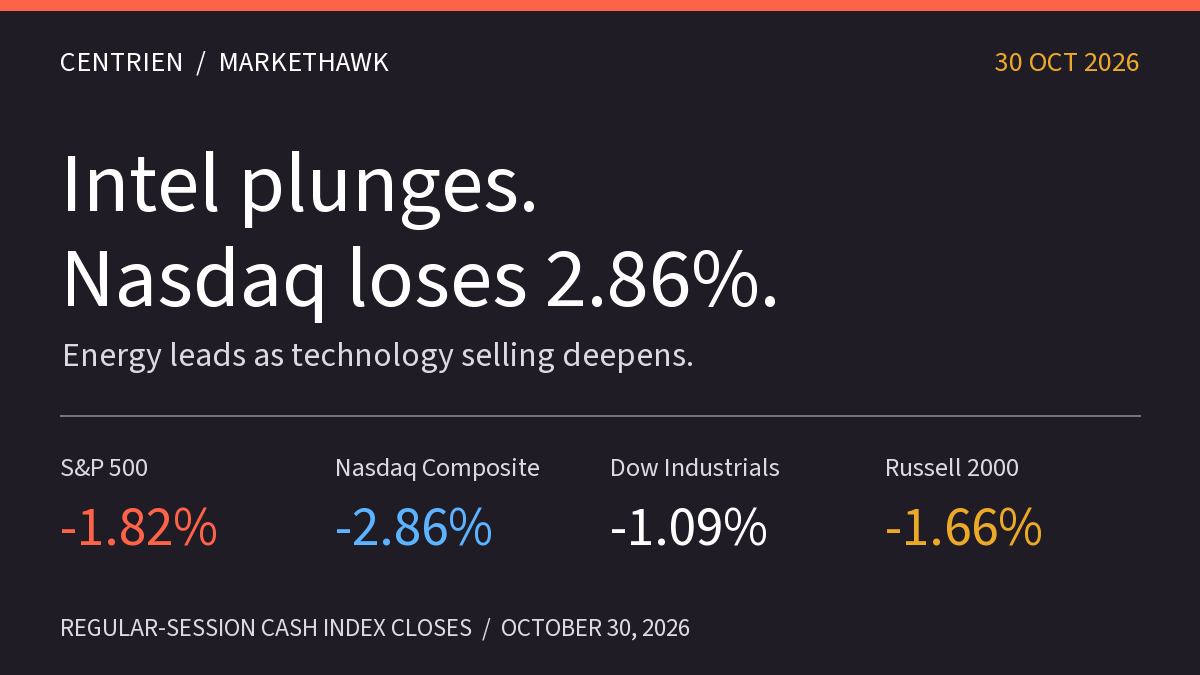
October 30 market close: Intel plunges, Nasdaq falls 2.86%
Intel falls 28.58% as its outlook weighs on technology. Nasdaq loses 2.86%, energy leads sector gains, and labor-cost data and weekly returns frame the Friday close.
4 min read →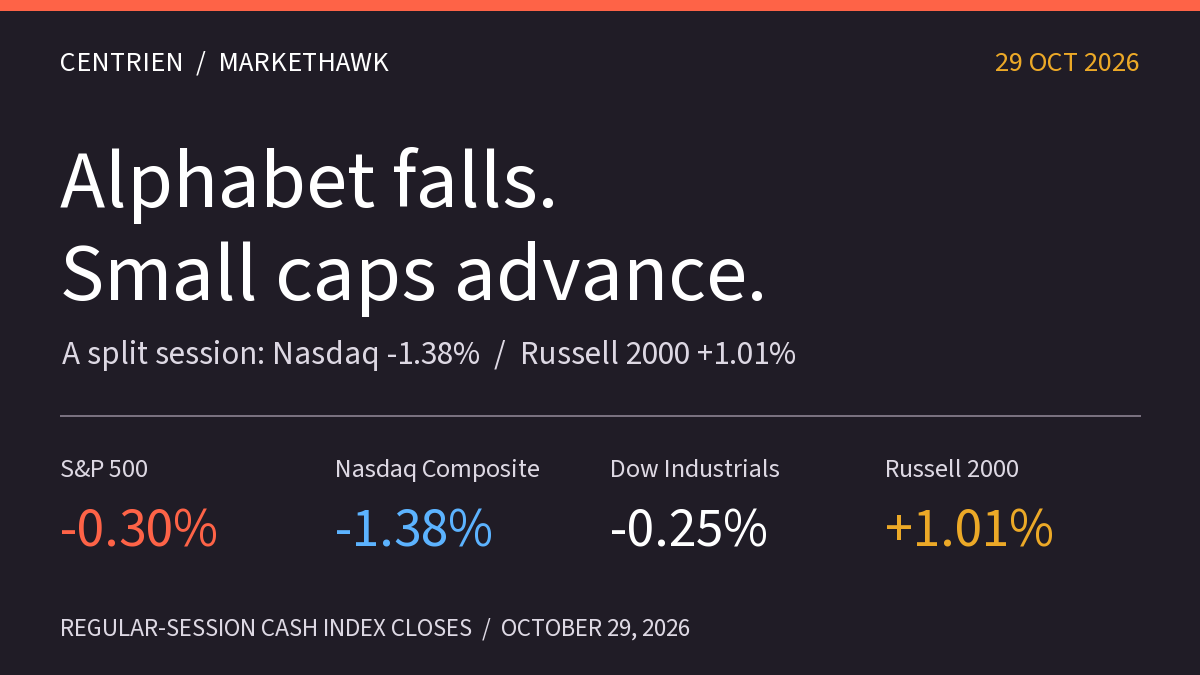
October 29 market close: Alphabet sinks, small caps advance
Alphabet falls 12.64% and the Nasdaq loses 1.38%, while small caps and nine sector ETFs gain. GDP, inflation and Amazon earnings frame a sharply divided session.
4 min read →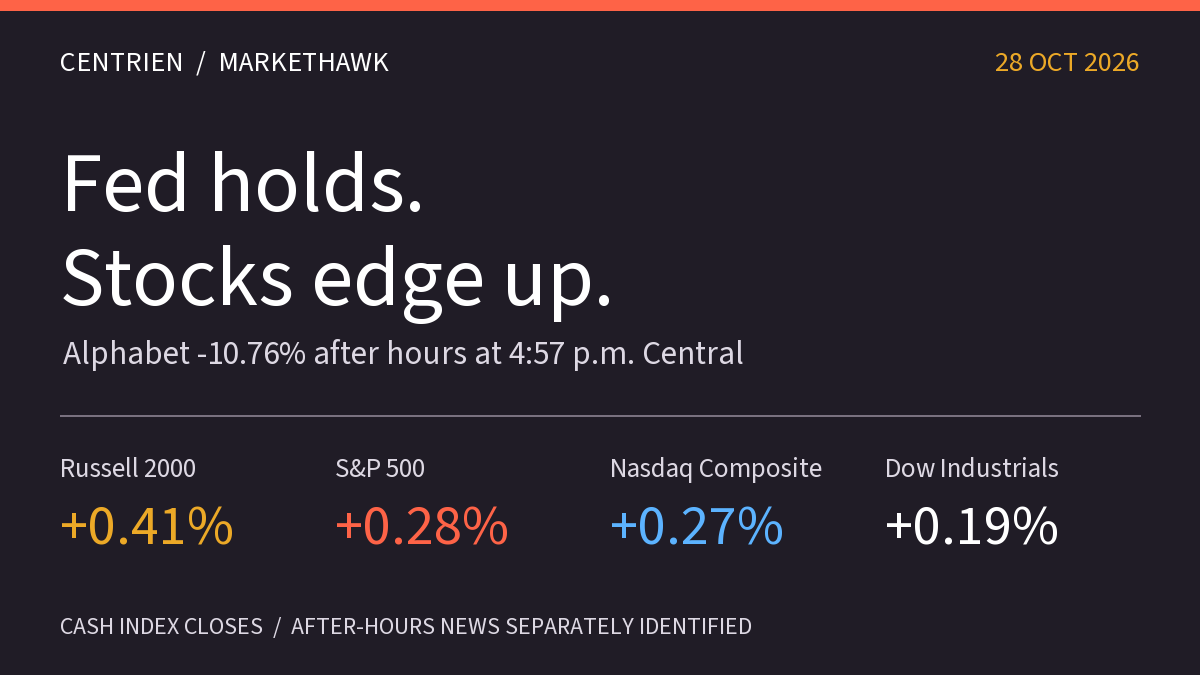
October 28 market close: Fed holds, Alphabet drops after hours
The Fed holds rates at 3.75%–4.00% in a split vote. Cash indexes edge higher, while Alphabet’s late after-hours decline sets a different test ahead of Thursday’s GDP and inflation data.
4 min read →
Holiday Retail Is a Security Event, Not Just a Sales Event
Seasonal retail planning brings temporary staff, changed hours, higher transaction demand, and more exceptions at the checkout. Security controls need to work under those operating conditions.
3 min read →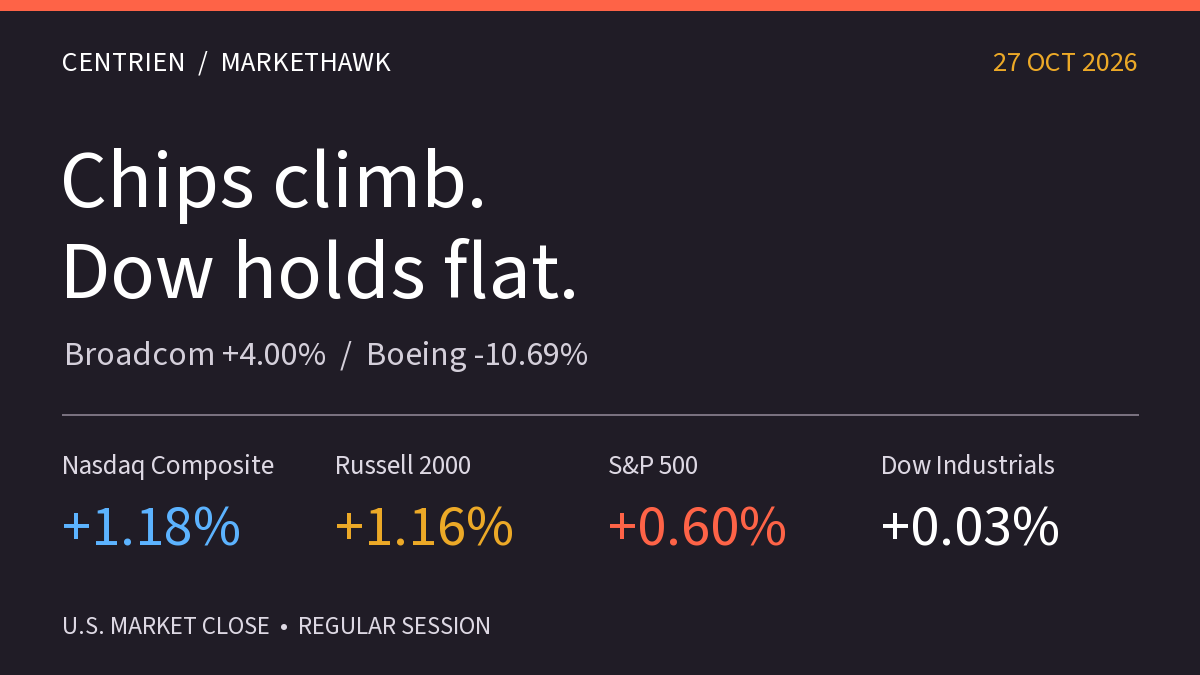
October 27 market close: Broadcom rallies, Boeing holds back Dow
The Nasdaq gained 1.18% and small caps rose 1.16%, while Boeing’s selloff left the Dow nearly flat. Broadcom financing, household data and Wednesday’s Fed decision frame the session.
4 min read →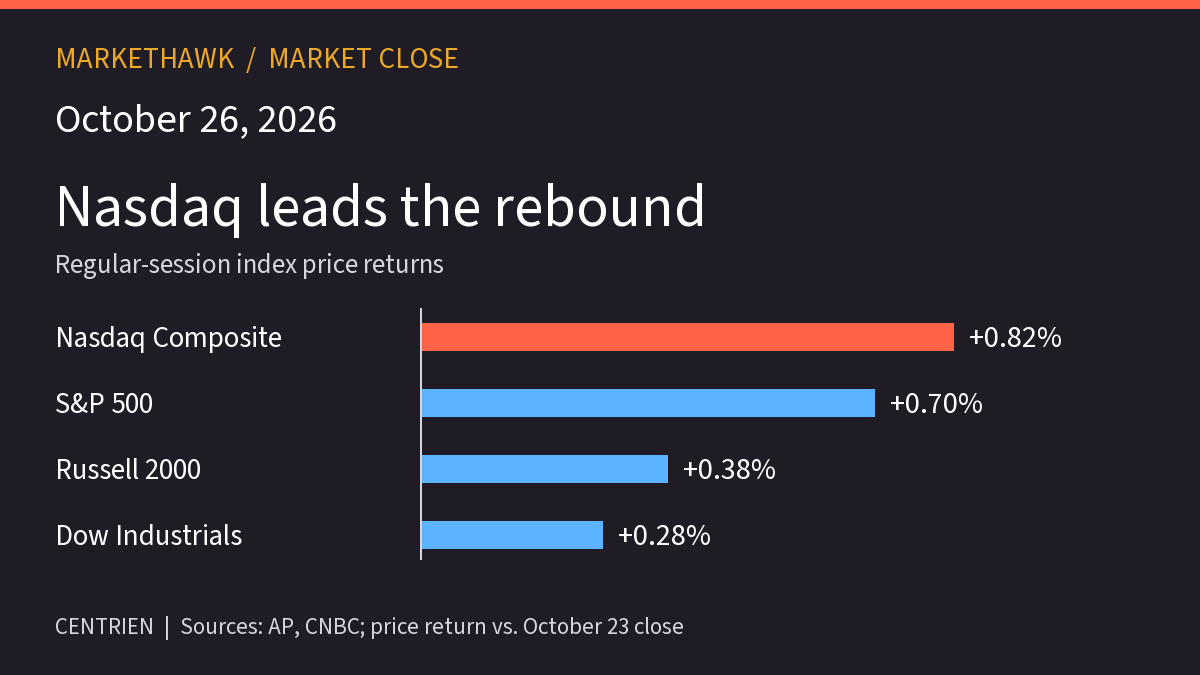
October 26 market close: Nasdaq leads as chip stocks rebound
Chip stocks led Monday’s rebound as the Nasdaq gained 0.82%. MarketHawk examines the sector split, oil and rates, and Tuesday’s confirmed calendar.
4 min read →
Read a Market Recap: Price Returns, Yields, and Session Times
A daily market recap can combine equity price returns, bond yields, commodity observations, and after-hours news. Those values answer different questions and may refer to different times.
4 min read →
A Clinical Downtime Drill That Tests the Work of Care
A clinical downtime drill needs to show how approved care workflows continue when a technology dependency is unavailable. Restoring an application is only one part of that exercise.
4 min read →
Write IT Acceptance Criteria a Public-Sector Team Can Test
An acceptance statement such as 'the system works' leaves the supplier and service owner to negotiate its meaning at the end of delivery. A testable requirement names the user, task, expected result, and conditions.
4 min read →
Test Your Technology Exit Before the Next Provider Renewal
An exit clause is useful when the institution can obtain usable records, restore the required service elsewhere, and remove the old provider's access. Each of those capabilities deserves a test before the renewal deadline.
4 min read →
School Account Offboarding: Protect Access When the Roster Changes
A roster change can disable a central account while leaving access in a classroom application, shared resource, or supplier-managed system. School offboarding needs to follow the person through those connected services.
4 min read →
The Education Sector’s Quiet Security Problem
School access changes as students move, staff change roles, and suppliers support individual applications. Shared devices and application-local accounts can leave gaps that a central sign-on list will not reveal.
3 min read →
Market Data You Can Trust: Signal, Not Noise
A market-data acceptance test should establish the instrument, observation time, market session, and calculation behind each value. More fields and faster delivery do not resolve a disagreement about those definitions.
3 min read →
Government IT Modernization Without the Headlines
Public-sector IT work needs visible ownership from procurement through service acceptance. A technical milestone should identify what people can now do and which dependencies remain unresolved.
3 min read →
The Clinic’s Guide to Documented HIPAA Security Readiness
A clinic's security review needs an accurate picture of electronic protected health information and the workflows that use it. Technical products and completed checklists can support the work, but they do not by themselves establish HIPAA compliance.
3 min read →
The Budget Conversation: Framing Technology as Risk, Not Cost
A technology budget request is easier to assess when it names the service exposure and the decision the funding changes. Cost reduction, risk treatment, and service improvement may all be legitimate reasons to invest.
3 min read →
The End-of-Year IT Checklist Nobody Enjoys but Everyone Needs
Renewals, support expiries, staffing changes, and recovery commitments can all create work before the calendar turns. A useful year-end review identifies the decisions that cannot safely wait.
4 min read →
Compliance Frameworks Are Converging. Map Once, Report Many.
Several assessments may ask about the same control, yet differ in system scope, reporting period, population, or method. A common control library can reduce duplication when those differences stay visible.
3 min read →
What a Real Disaster Recovery Test Looks Like
A restored server can be healthy while the business remains unable to work. Identity, application dependencies, data consistency, and the people who authorize service release all belong in a disaster recovery test.
4 min read →
Refrigeration Alarms at 2 A.M.: Building a Response Plan That Works
A refrigeration alarm needs to reach someone who can assess the situation and arrange a response. The contact list has to work during the hours when the normal site team is unavailable.
3 min read →
The Hidden Cost of Running POS and Payments on Separate Vendors
A payment dispute can cross the POS application, terminal, processor, network, and store procedures. Separate suppliers are manageable when that chain has a clear lead and records that allow the transaction to be reconciled.
3 min read →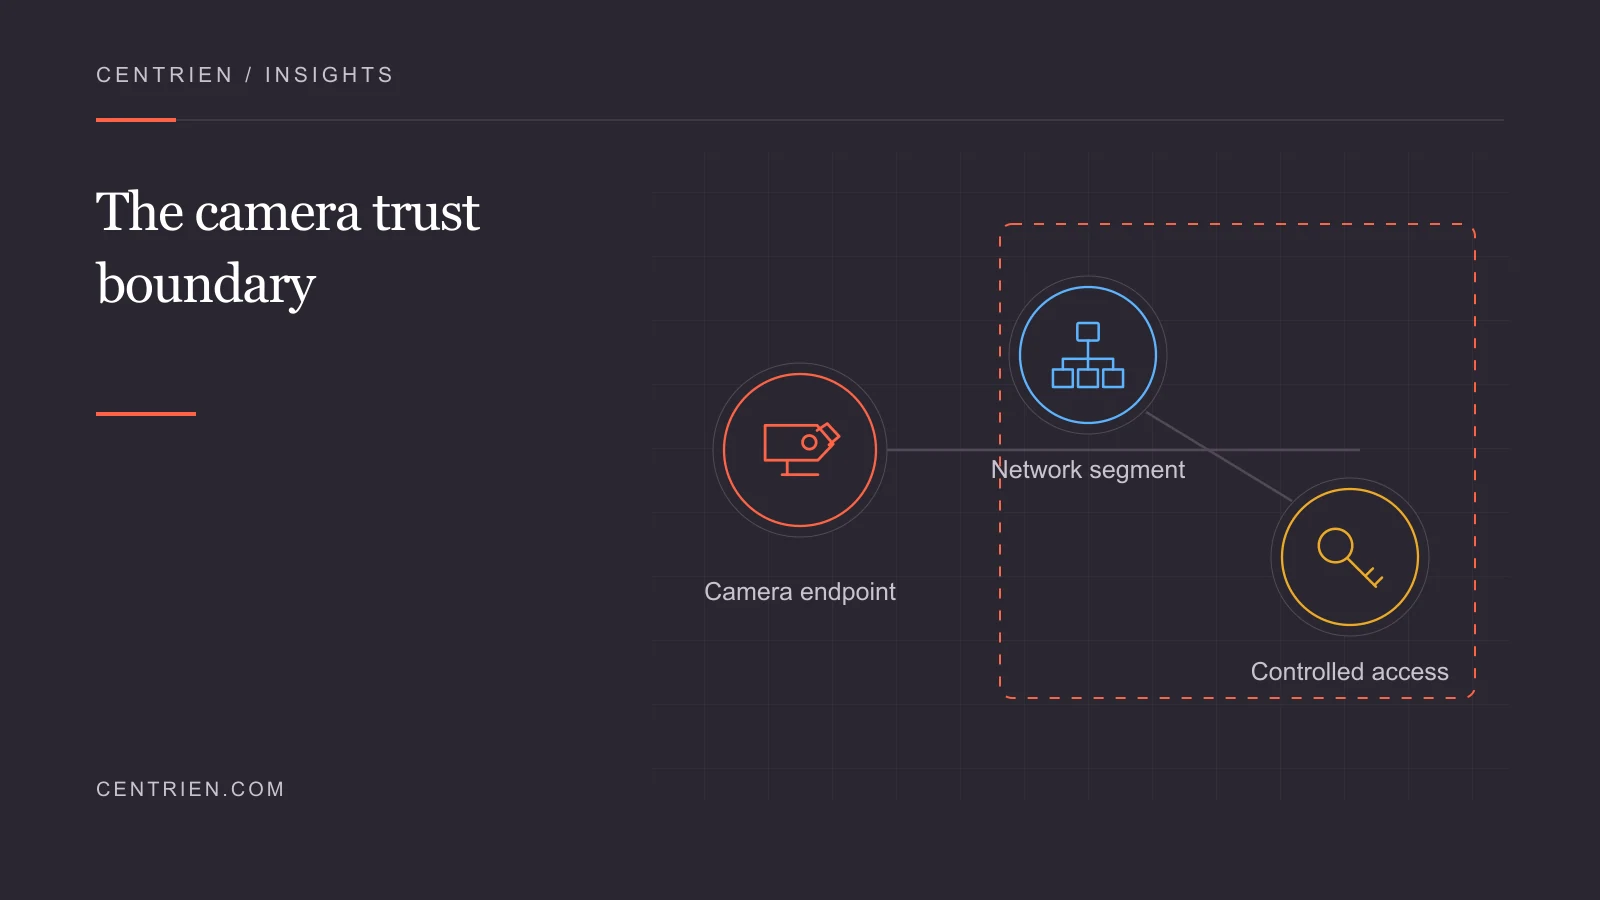
When Your Security Camera Becomes Your Weakest Network Link
A network camera has software, credentials, remote access, and a support lifecycle. Installation is the beginning of that responsibility; the device still needs an owner after the installer leaves.
4 min read →
Migrating Off Microsoft Dynamics RMS: A Verified Store Cutover Plan
Moving away from Microsoft Dynamics RMS requires more than a successful item import. The replacement needs to reproduce the store's approved pricing, taxes, tenders, returns, inventory movements, and end-of-day records.
3 min read →
How AI is transforming the security operations center
An AI assistant can help organize alert context or draft an investigation summary. Its value depends on whether the analyst reaches a sound decision with less effort, and whether the system keeps sensitive data and response permissions within the intended boundaries.
3 min read →
Predictive maintenance: how AI keeps refrigeration running
A refrigeration sensor may reveal a change in temperature or equipment behavior. Predictive maintenance adds value when that observation leads to a justified inspection or repair with enough time to matter.
3 min read →
Real-time market data in the age of AI
Two screens can show different values for the same instrument without either number being a simple error. Observation time, market session, currency, adjustments, and return methodology can all change what the number means.
3 min read →
AI at the point of sale: smarter, safer retail
A retail AI proposal needs a specific job: identify an inventory discrepancy, help review a transaction, or answer a defined operating question. Each job has different data needs, error costs, and approval requirements.
3 min read →
Using AI to stay continuously audit-ready
Automating evidence collection can reduce time spent finding records. It does not establish that the control worked, that the population was complete, or that an exception was resolved.
3 min read →
Public-Sector IT Modernization: Protect the Service During Migration
A public-sector migration needs a clear account of the service people rely on, including the exceptions and assisted routes that may be easy to miss in a technical design. That service should shape the delivery plan.
3 min read →
AI video analytics: from watching to knowing
A video analytics proposal should name the event it is intended to detect and the response that follows. A count, an unusual movement, and an intrusion alert require different tests and different privacy decisions.
3 min read →
Protecting patient data: a practical security primer
Patient information moves through registration, care delivery, billing, support, and supplier systems. Protecting it starts with understanding those paths and the access needed at each stage.
3 min read →
Why multidisciplinary beats best-of-breed for the mid-market
Specialist suppliers can bring depth that a business needs. An integrated provider can simplify coordination. The practical comparison is how each arrangement handles the work between disciplines, especially when an incident crosses several contracts.
3 min read →
Five questions to ask before your next vendor renewal
A renewal date creates a useful opening to review what the supplier actually delivers. Service records, unresolved incidents, export tests, and support handoffs give procurement a stronger starting point than last year's contract alone.
3 min read →
The connected campus: safety, IT, and everything between
Campus technology supports teaching, administration, communications, and physical safety. Shared infrastructure can simplify support, but it also creates dependencies that need clear boundaries and ownership.
3 min read →
Preventative maintenance math: what downtime really costs
A repair invoice captures only part of an equipment failure. The same interruption may require emergency labor, inventory disposal, temporary equipment, or reduced trading hours. Those costs belong in the maintenance decision.
3 min read →
Getting audit-ready without the fire drill
An assessment request becomes difficult when the team has to recreate months of activity from scattered emails and screenshots. Keep the records of a control's operation as part of the work that produces them.
3 min read →
Why financial institutions are consolidating technology partners
Fewer technology suppliers can simplify support and procurement. They can also place more services behind the same provider, making an outage or difficult exit more consequential.
3 min read →
Modernizing POS without disrupting the floor
A POS upgrade changes more than the register screen. Pricing, tax, tenders, returns, inventory, and daily reconciliation all need to work together before the store accepts the new system.
3 min read →
Physical and digital security are converging
A door controller or network camera depends on power, connectivity, accounts, and software. When it stops working or behaves unexpectedly, the physical security and IT teams may each hold only part of the explanation.
3 min read →
Value Engineering: Compare Lifecycle Cost Without Losing Required Performance
A cheaper component or delivery method can be a sound engineering choice. The saving needs to survive installation, operation, maintenance, and eventual replacement, while the proposed design continues to meet applicable requirements.
3 min read →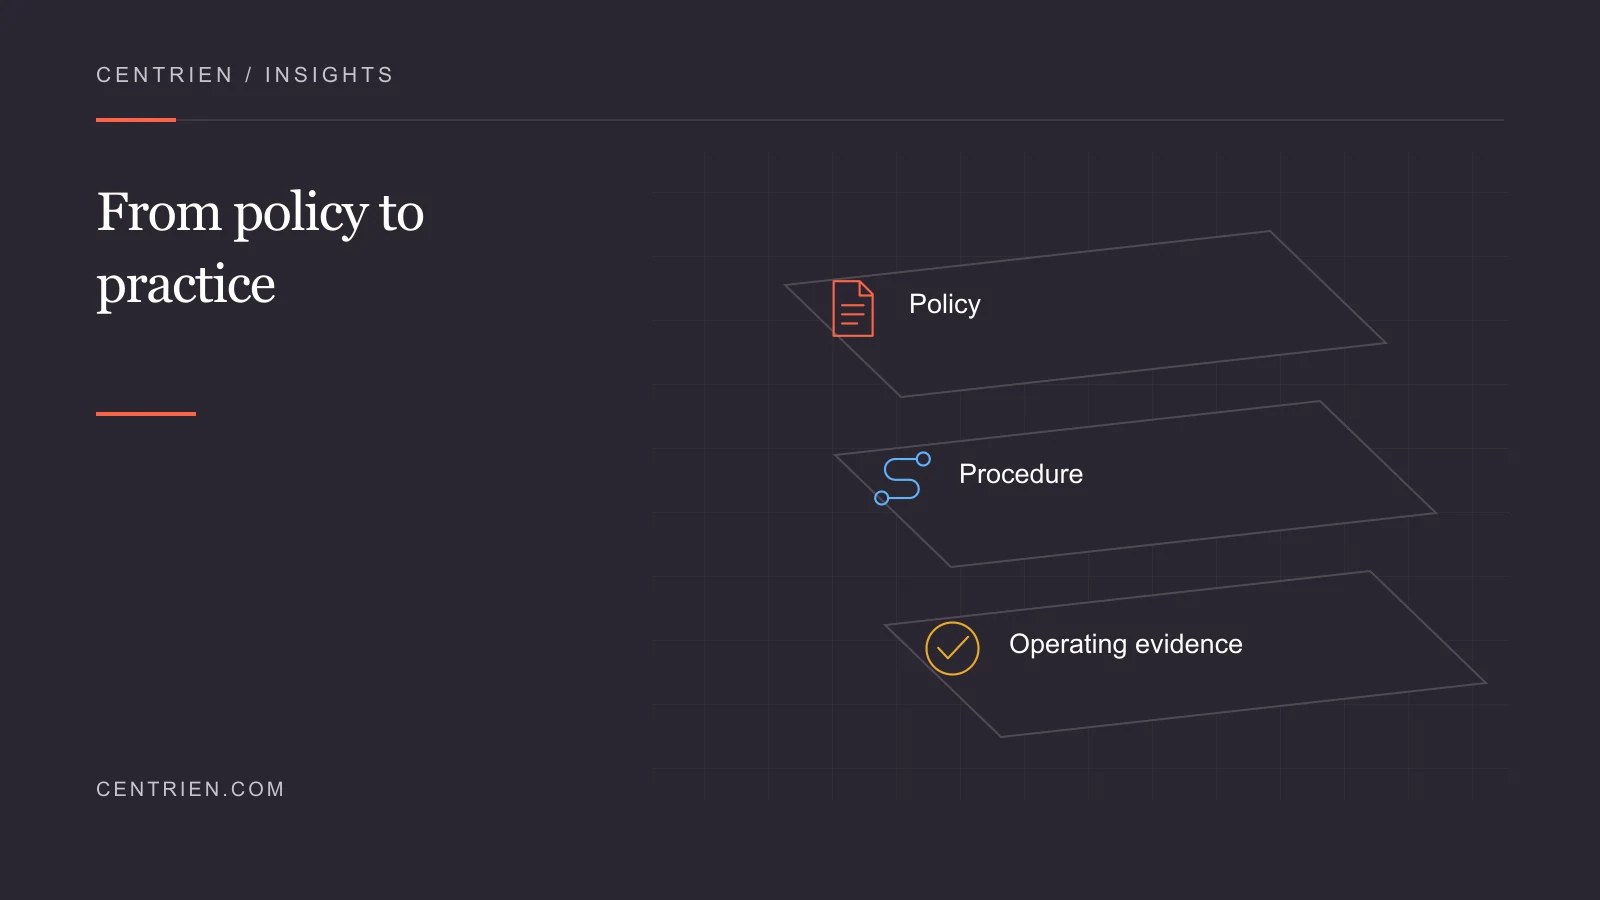
Policies, Standards, Procedures, and Plans: Give Each a Clear Purpose
People need different answers from a policy and a procedure. A policy states management's intent. A standard sets mandatory requirements. A procedure describes the steps to carry out a task, while a plan organizes a response or a course of work.
3 min read →
Securing Developer Publishing Accounts: Ownership, MFA, and Recovery
The person who controls a developer publishing account may be able to release software to every customer. Account ownership, automation credentials, and recovery methods therefore deserve the same attention as the production environment.
3 min read →
A Safer Social Publishing Workflow: Claims, Permissions, and Corrections
A social post can be accurate in its wording and still send readers to the wrong page. It can also expose a customer name or account detail hidden in a screenshot. Review the complete post, including the image and the link destination.
3 min read →
Package Maintainer Changes: A Practical Supply-Chain Review
A maintainer handover deserves a review because it changes who can influence a dependency. The handover alone does not establish that a package is unsafe. The release, its permissions, and the applications using it need closer inspection.
3 min read →
Workplace Cybersecurity: A Practical Baseline You Can Verify
An employee who cannot reach email, a shared file, or a customer application has an immediate problem. A workplace security baseline needs to protect those services and give staff a clear route to help when something looks wrong.
3 min read →Bring your priorities.
Let’s build the next step.
Discuss your requirements with Centrien and connect the right expertise around your operation.
