Look closely at the handoffs
Specialist suppliers can bring depth that a business needs. An integrated provider can simplify coordination. The practical comparison is how each arrangement handles the work between disciplines, especially when an incident crosses several contracts.
Trace a recent service issue from the user through the application, network, security controls, and any site equipment involved. Identify the coordination your staff performed. Include that work, the relevant expertise, and exit arrangements in the supplier comparison.
Put it into practice
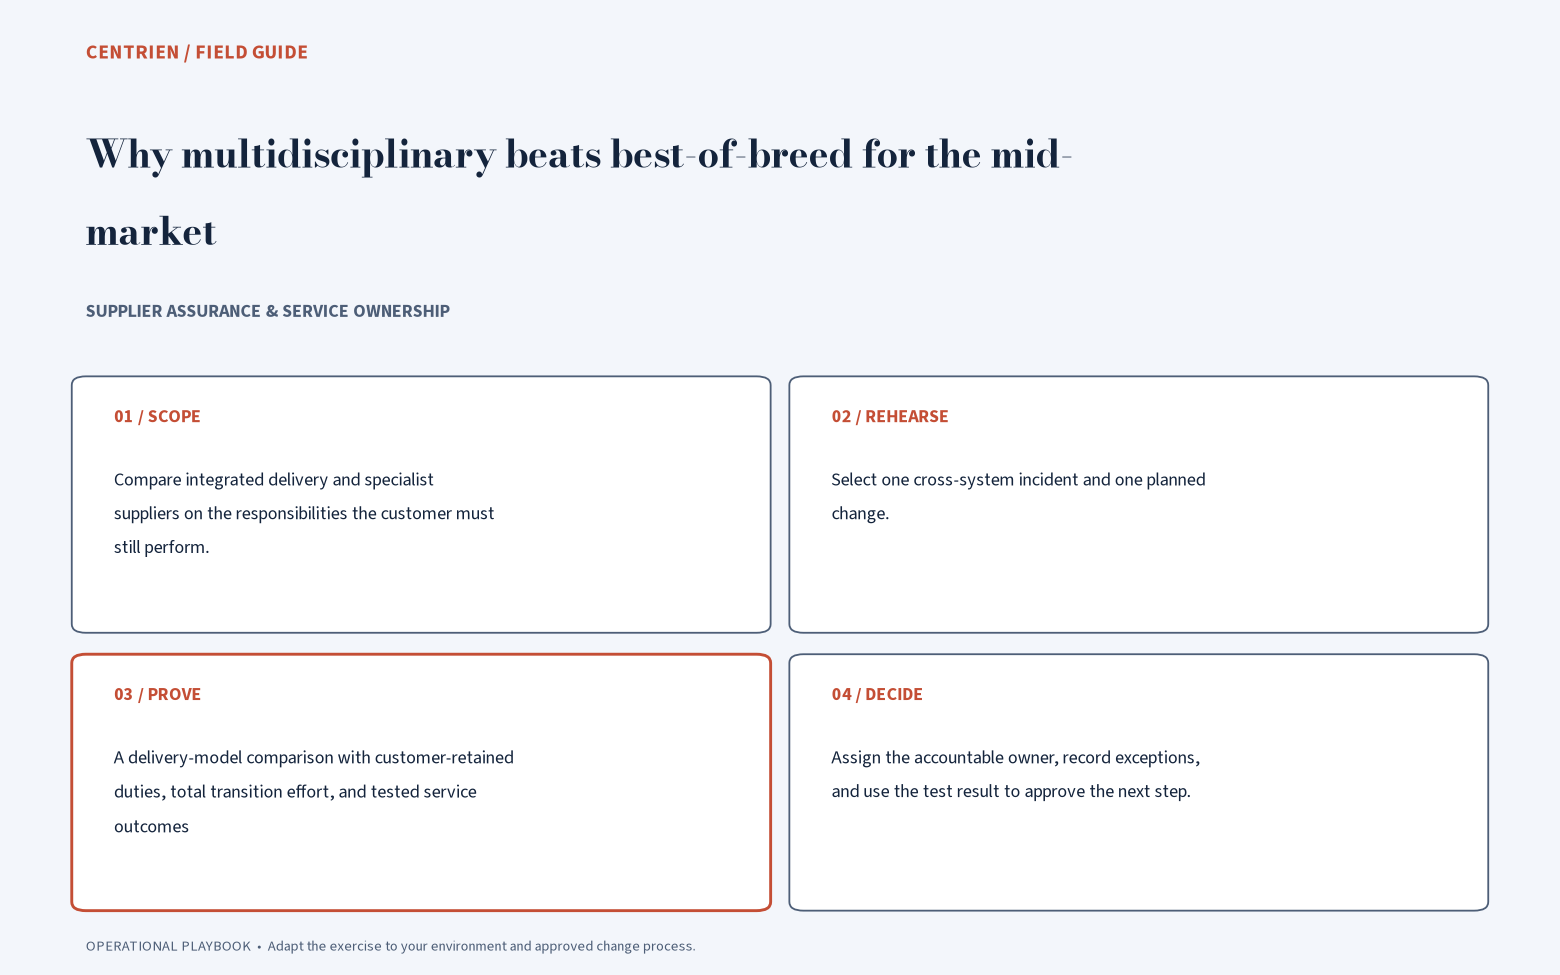
Select one cross-system incident and one planned change. Compare escalation paths, integration work, independent checks, concentration risks, and contract exclusions. Ask each model to demonstrate a recovery exercise involving all relevant components.
Implementation steps
- Map the dependencyList the business service, supplier access, data handled, subcontractors, and interfaces. Distinguish the provider contract from the responsibilities that remain with the customer.
- Ask for scoped evidenceRead the period, system boundary, exceptions, and customer obligations in assurance material. Use a targeted demonstration or agreed exercise to investigate material gaps without requesting indiscriminate access.
- Rehearse the handoffRun a controlled incident or change across the supplier boundary. Verify acknowledgement, decision authority, data access, restoration responsibilities, and the point where another party must take over.
- Test the exitExport representative data, verify its completeness and usability, and identify replacement dependencies. Record retention and access-removal obligations so an exit plan is more than a termination clause.
Track critical dependency ownership and assurance coverage
| Measure | Calculation or definition | How to use it |
|---|---|---|
| Critical dependency ownership | Critical supplier services with a business owner / critical supplier services | Escalate services whose risk nobody can accept. |
| Assurance coverage | Material supplier scenarios with current evidence / material scenarios reviewed | Separate a missing document from a tested control failure. |
| Exit readiness | Critical data exports successfully reconciled / exports tested | Retest after material format, scope, or service changes. |
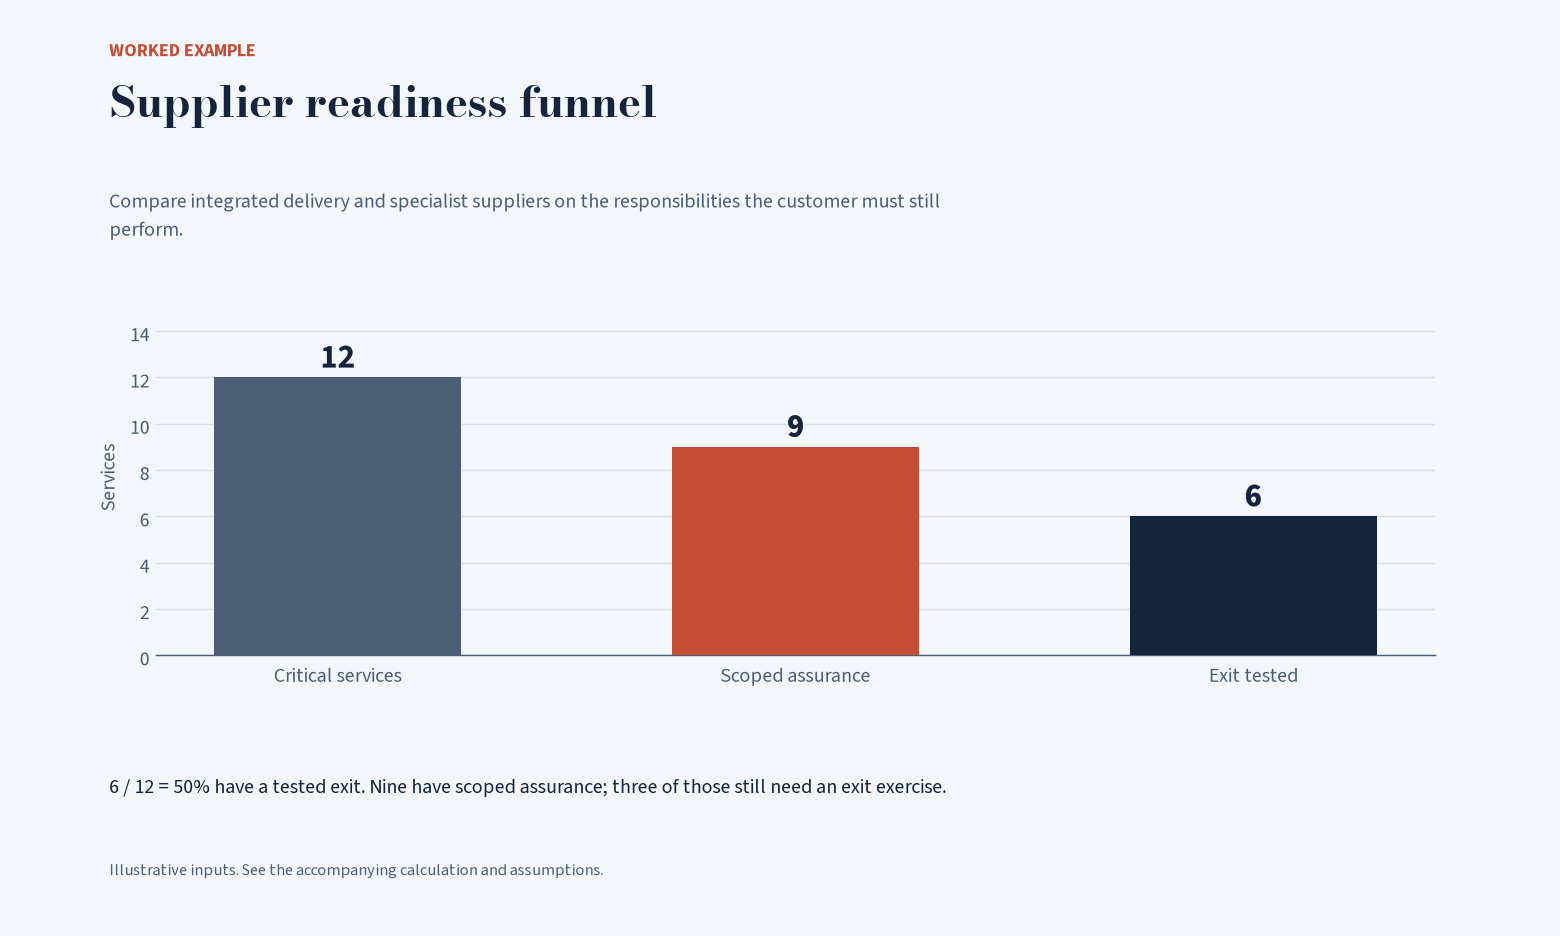
Supplier readiness funnel
Worked example. Figures are illustrative.
| Observation | Services |
|---|---|
| Critical services | 12 |
| Scoped assurance | 9 |
| Exit tested | 6 |
A contract signature or questionnaire score is not counted as an executed exit test.
The record to keep
The deliverable: A delivery-model comparison with customer-retained duties, total transition effort, and tested service outcomes.
Choose the delivery model against a real service scenario. Require the proposed providers to explain who leads diagnosis and how they resolve a dispute over the cause.
References
- NIST Cybersecurity Framework — Use outcomes and organizational context to organize the risk discussion; a framework mapping is not a control test.
- NIST SP 800-34 Rev. 1: Contingency Planning — Use impact analysis, recovery priorities, exercises, and plan maintenance to structure continuity work.
Keep reading.
Your Access List Is a Museum. Time to Clean It Out.
An access review needs more than a list of active employees. Supplier accounts, service identities, inherited permissions, and active sessions can preserve access after the original reason has ended.
3 min read →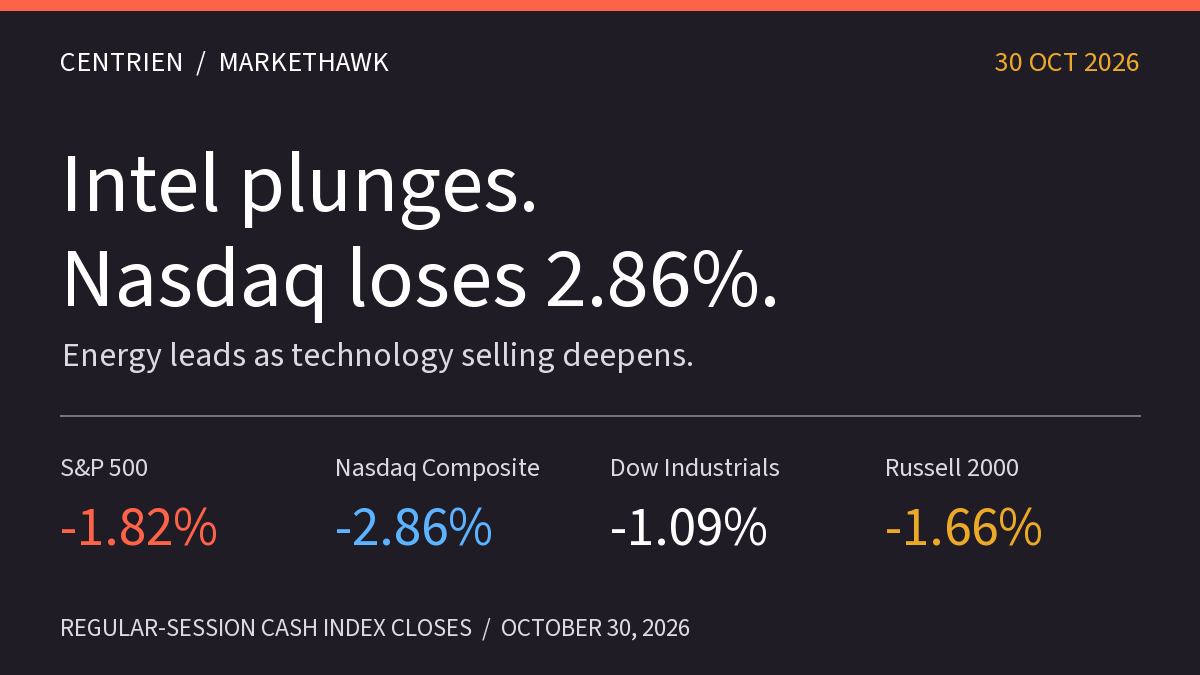
October 30 market close: Intel plunges, Nasdaq falls 2.86%
Intel falls 28.58% as its outlook weighs on technology. Nasdaq loses 2.86%, energy leads sector gains, and labor-cost data and weekly returns frame the Friday close.
4 min read →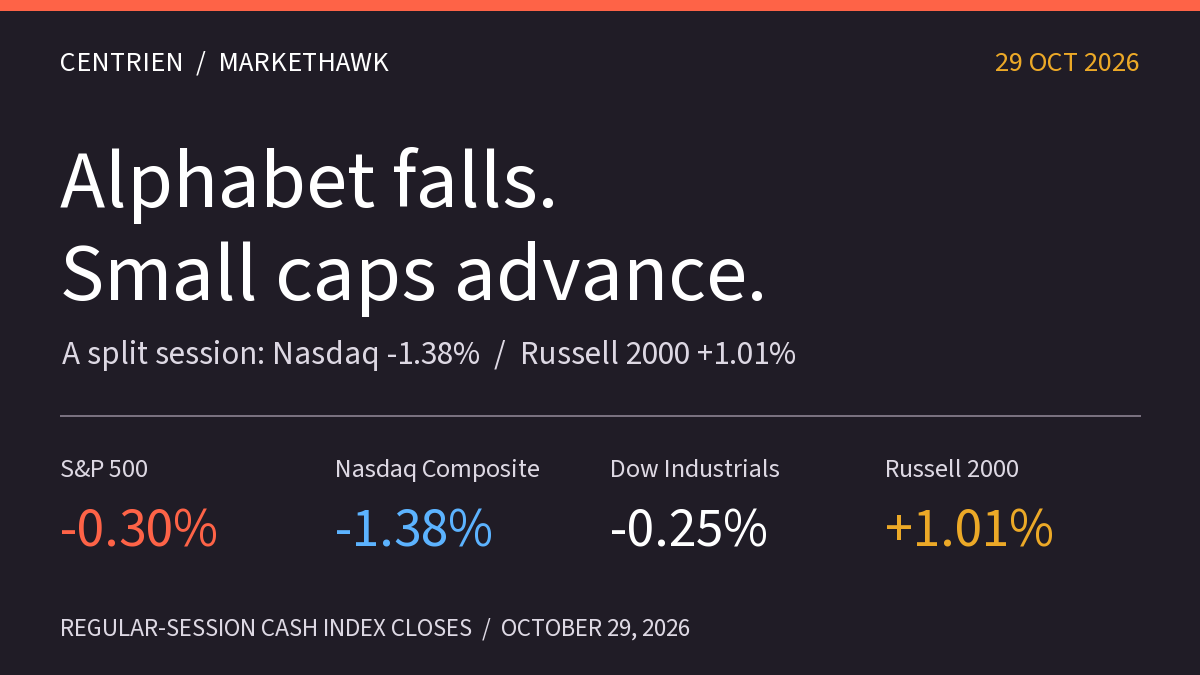
October 29 market close: Alphabet sinks, small caps advance
Alphabet falls 12.64% and the Nasdaq loses 1.38%, while small caps and nine sector ETFs gain. GDP, inflation and Amazon earnings frame a sharply divided session.
4 min read →