Start with the work people need to do
An employee who cannot reach email, a shared file, or a customer application has an immediate problem. A workplace security baseline needs to protect those services and give staff a clear route to help when something looks wrong.
Choose a business process and follow it through the devices, accounts, applications, and suppliers involved. Check who supports each dependency, how access is removed, and whether the data can be recovered. A short service map is more useful here than an inventory of products with no owner attached.
Put it into practice
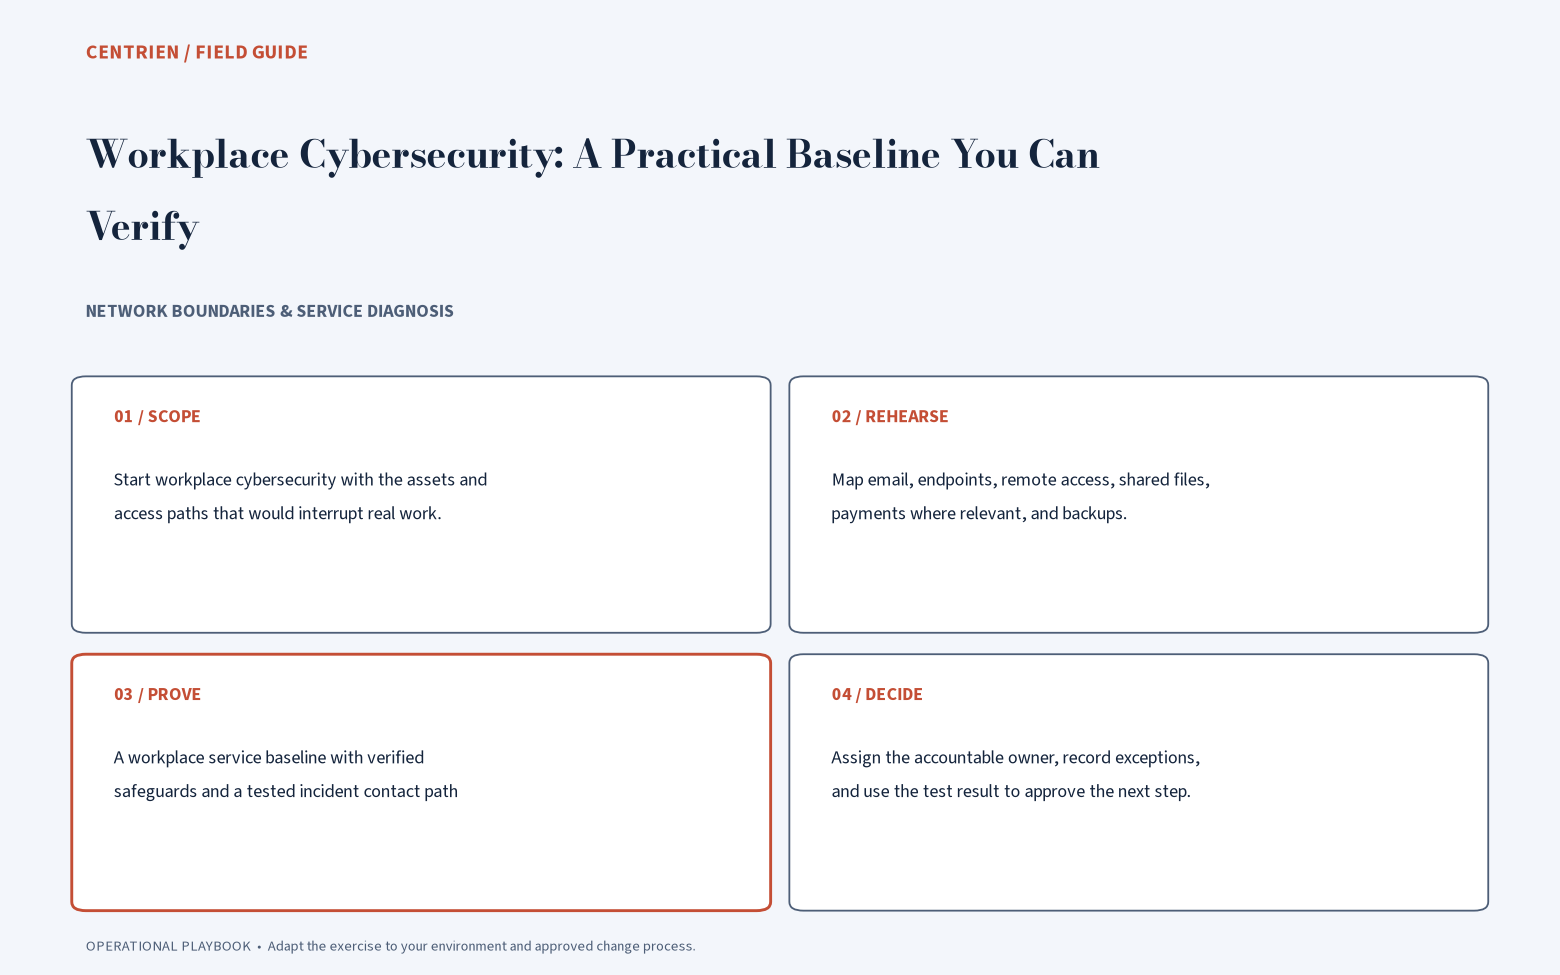
Map email, endpoints, remote access, shared files, payments where relevant, and backups. Verify authentication, patch ownership, logging, and a recoverable copy of critical data. Rehearse how employees report an incident and continue essential work.
Implementation steps
- Map intended flowsRecord endpoints, network zones, service ports, remote administration, identity dependencies, and business owners. Include cameras, appliances, guest access, and vendor paths where they affect the service.
- Verify the baselineCheck supported versions, administrative access, configuration backups, clock synchronization, and telemetry. Reproduce one legitimate workflow so later changes can be compared with a known working state.
- Constrain and testApply approved segmentation or access changes in a controlled window. Test both a required connection and a prohibited route. Preserve local or emergency operation for safety-dependent equipment.
- Prove the handoffCollect correlated timestamps from the application, endpoint, network, and circuit provider. Define who owns the next diagnostic step and verify configuration recovery before declaring the incident resolved.
Track flow validation and device ownership
| Measure | Calculation or definition | How to use it |
|---|---|---|
| Flow validation | Required and denied paths verified / paths in the approved matrix | Include administrative and vendor routes, not only user traffic. |
| Device ownership | In-scope devices with support owners / devices discovered | Investigate unsupported equipment and unidentified remote access. |
| Recovery coverage | Critical configurations restored successfully / configurations tested | A saved configuration is weaker evidence than a successful restore. |
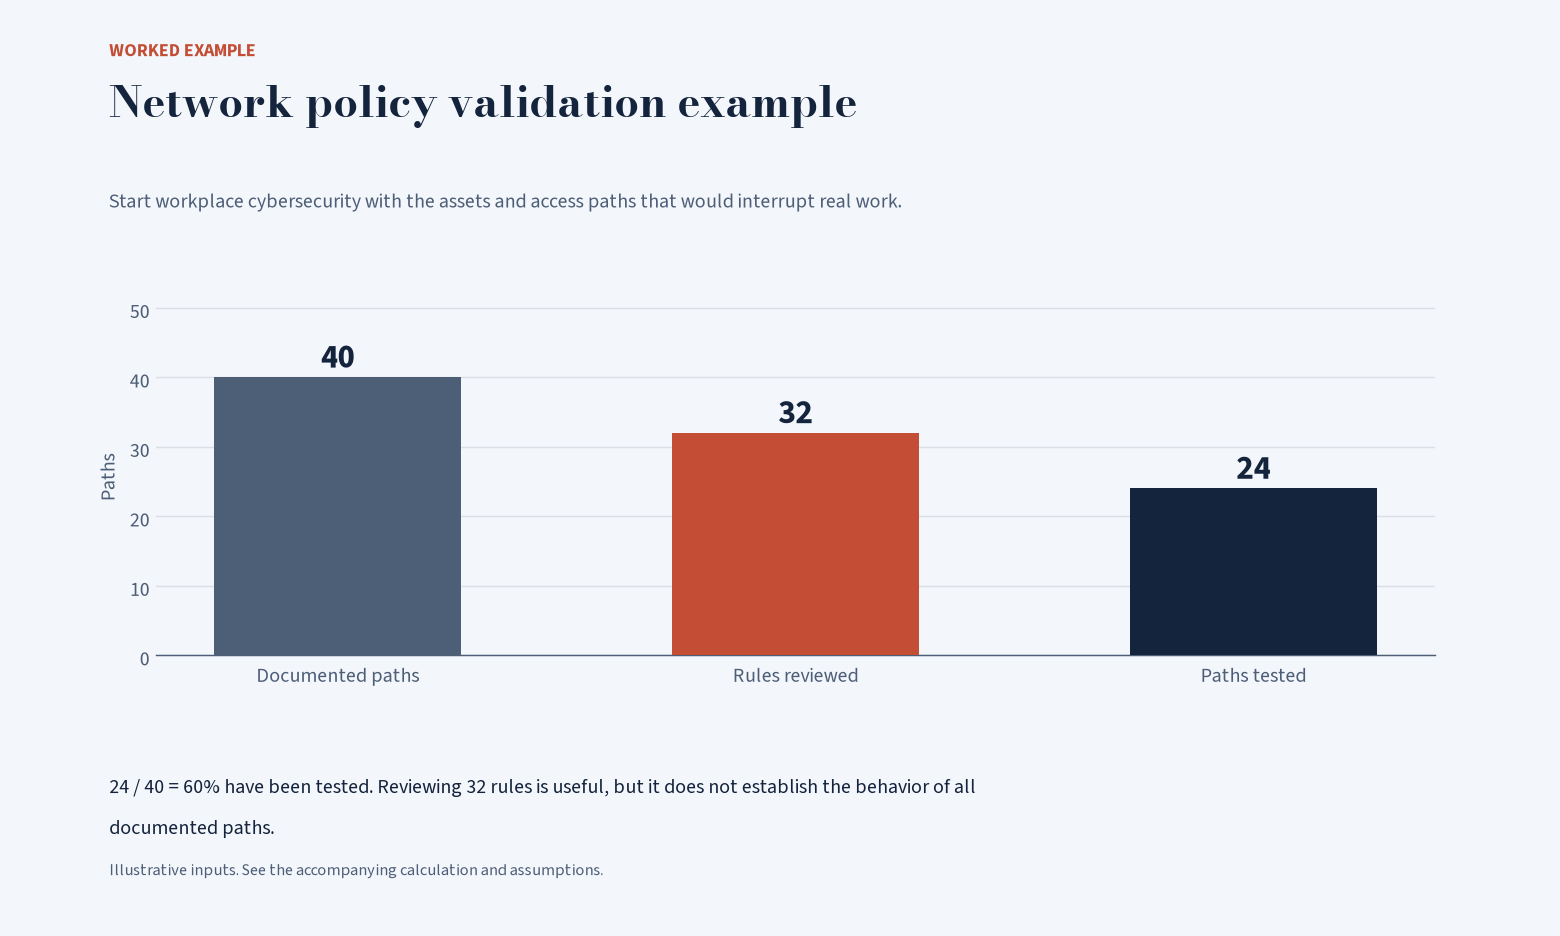
Network policy validation example
Worked example. Figures are illustrative.
| Observation | Paths |
|---|---|
| Documented paths | 40 |
| Rules reviewed | 32 |
| Paths tested | 24 |
Test allowed and denied paths against the approved network policy.
The record to keep
The deliverable: A workplace service baseline with verified safeguards and a tested incident contact path.
Ask a colleague to report a harmless test issue through the published support route. Follow it to resolution, then fix any handoff that leaves the employee waiting without an owner.
References
- NIST SP 800-207: Zero Trust Architecture — Treat access to resources as an explicit policy decision rather than trust inherited from network location.
- NIST SP 800-82 Rev. 3: Operational Technology Security — Adapt security work to operational technology performance, reliability, and safety requirements.
Keep reading.
Your Access List Is a Museum. Time to Clean It Out.
An access review needs more than a list of active employees. Supplier accounts, service identities, inherited permissions, and active sessions can preserve access after the original reason has ended.
3 min read →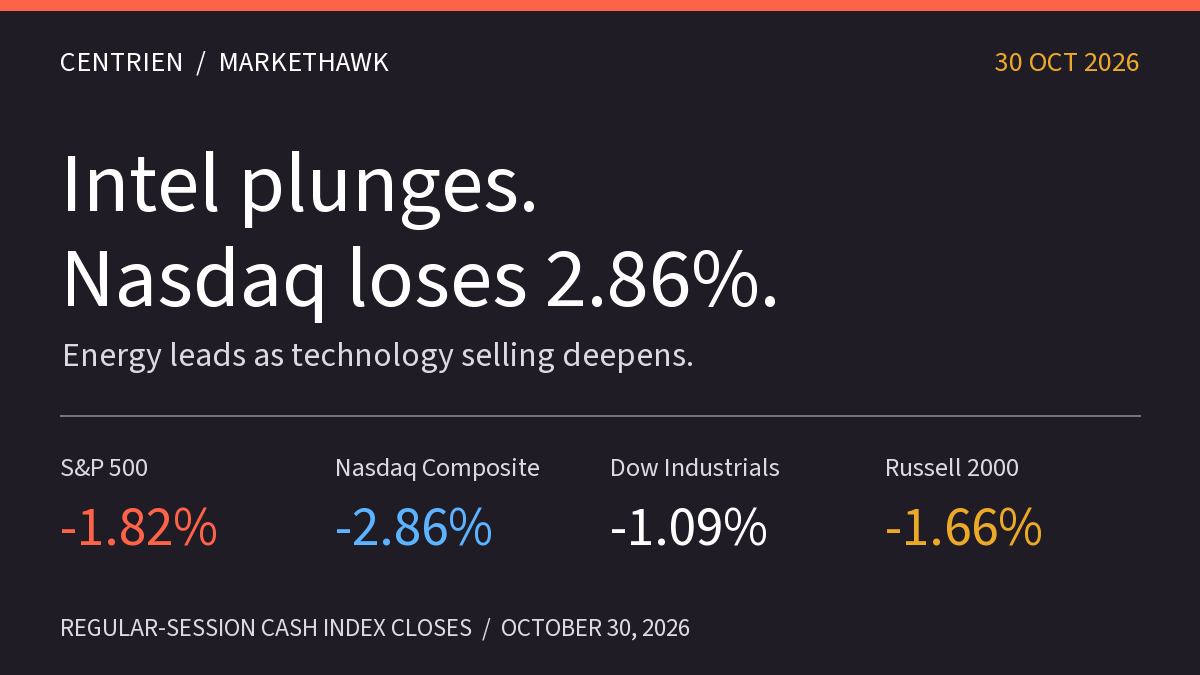
October 30 market close: Intel plunges, Nasdaq falls 2.86%
Intel falls 28.58% as its outlook weighs on technology. Nasdaq loses 2.86%, energy leads sector gains, and labor-cost data and weekly returns frame the Friday close.
4 min read →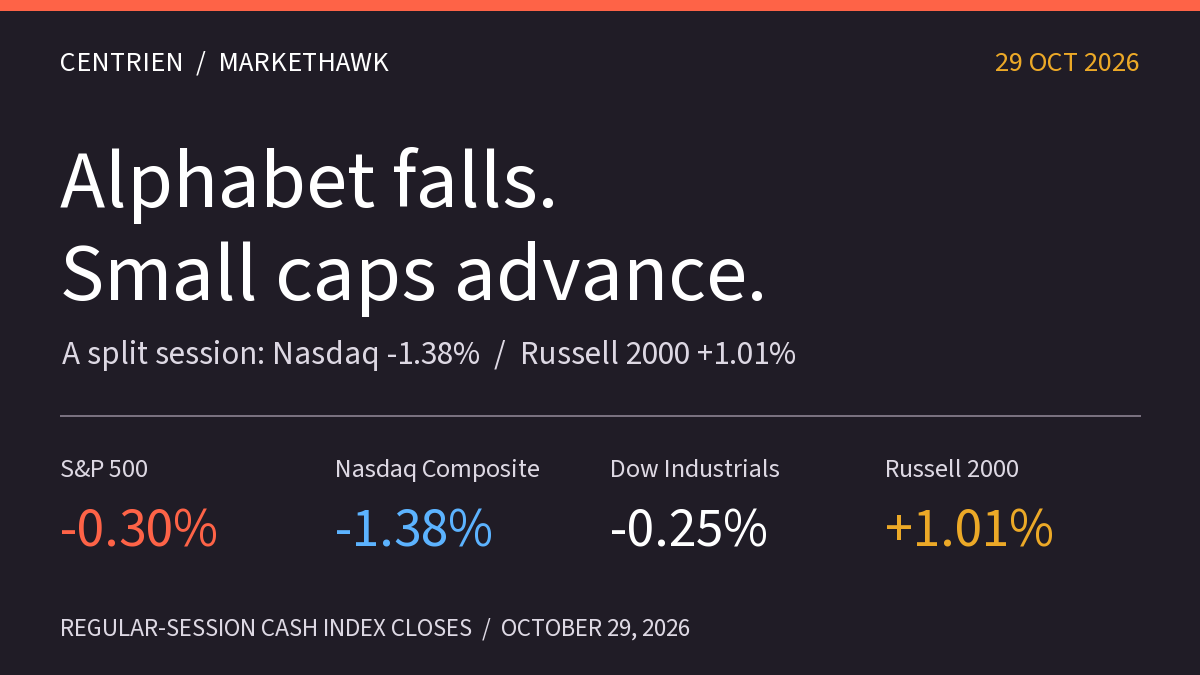
October 29 market close: Alphabet sinks, small caps advance
Alphabet falls 12.64% and the Nasdaq loses 1.38%, while small caps and nine sector ETFs gain. GDP, inflation and Amazon earnings frame a sharply divided session.
4 min read →