Why it matters
If you serve more than one industry or more than one large customer, you have felt the compliance tax: SOC 2 for one client, HIPAA for another, PCI for payments, a state privacy law on top, and a security questionnaire that reinvents all of it in a spreadsheet. Teams answer the same questions a dozen different ways and call it a program.
The quiet truth about frameworks
Most of these frameworks are asking the same questions in different clothes. Access control, encryption, logging, vendor management, incident response, backups — the controls underneath are largely shared. What differs is the vocabulary and the evidence format, not the substance. When you treat each framework as a separate project, you rebuild the same wall over and over and never finish any of them.
Map once, report many
The better model is a single control framework that you implement once and then map outward to each standard you have to satisfy. You define a control — say, “privileged access is reviewed quarterly” — implement it properly, and then point it at SOC 2, HIPAA, PCI, and the questionnaire simultaneously. One control, many citations. Evidence collected once answers every audit that asks for it.
This is the whole idea behind our Praxis approach: one framework, mapped to the global standards and laws you actually face, so your team proves a control exists instead of re-deriving it for every auditor. The work moves from frantic, audit-driven fire drills to a steady operating rhythm where you are continuously audit-ready and the next assessment is a matter of exporting evidence, not building it.
The organizations that drown in compliance are usually not under-controlled. They are under-mapped — doing the same work many times because nothing connects it. Map the control once, satisfy the frameworks many times, and compliance stops being the thing that consumes every quarter.
If your team is answering the same security question in three formats this month, that duplication is the opportunity. Consolidate it.
Put it into practice
The practical starting point
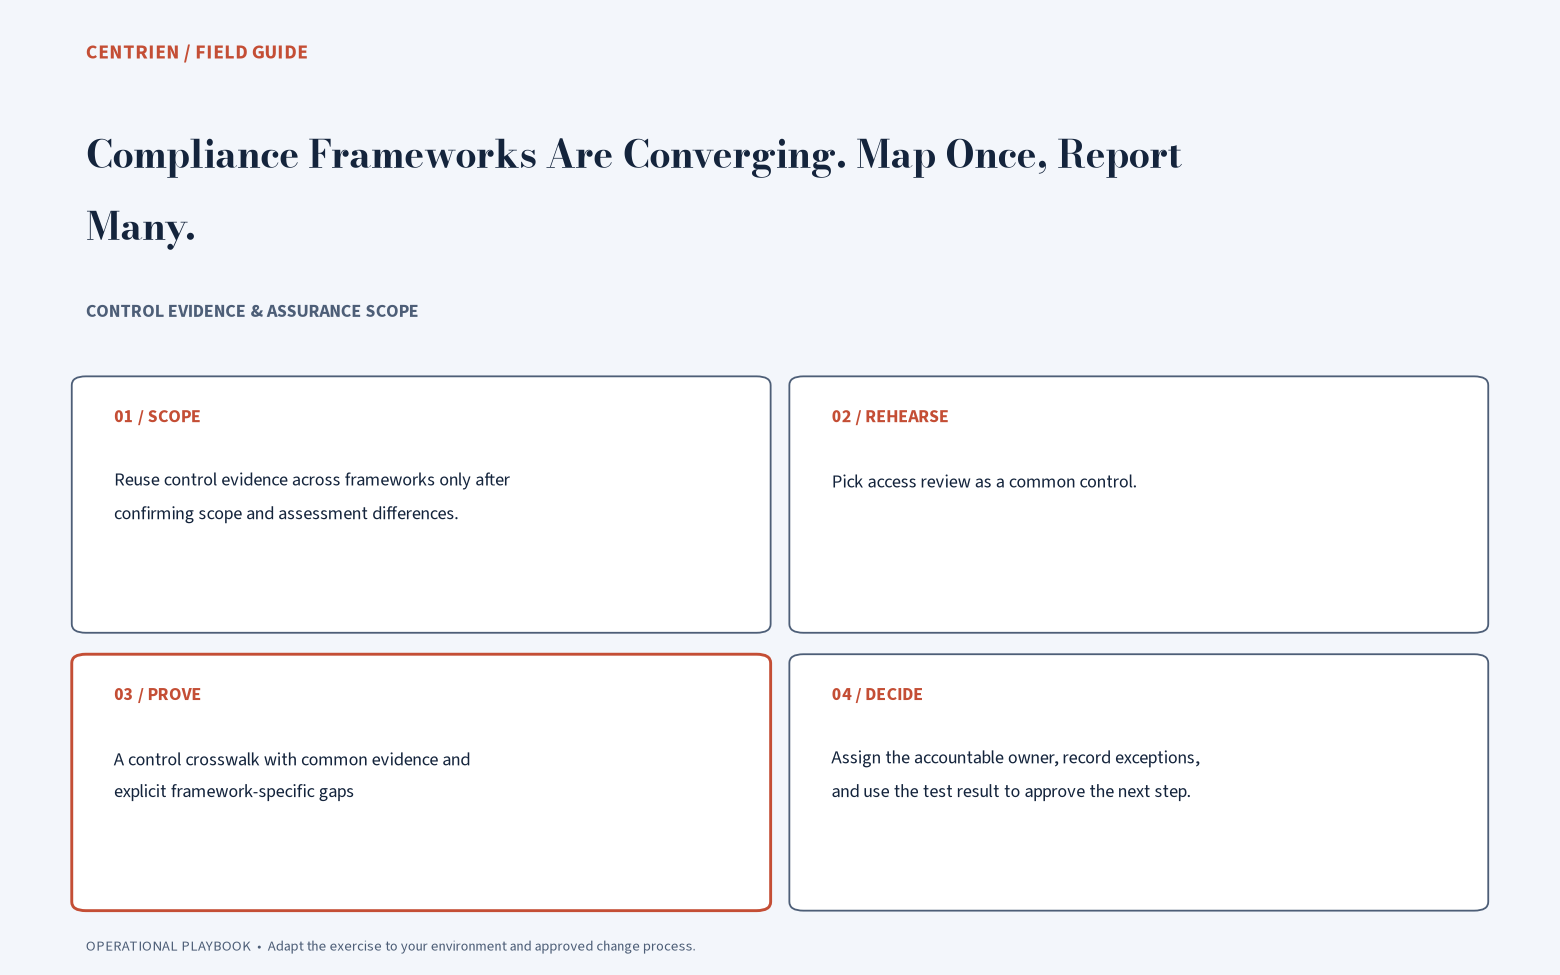
Pick access review as a common control. Map its objective to each applicable requirement, then record populations, review periods, exceptions, and assessor expectations separately. Reuse the underlying source record while retaining each obligation’s interpretation.
Implementation steps
Use this sequence to assign responsibilities, test controls, and document outcomes. Set the scope and acceptance criteria for the service before you begin.
- Read the obligationIdentify the applicable requirement, service boundary, assessment period, and responsible legal entity. Distinguish mandatory obligations from voluntary guidance and contractual expectations.
- Define the control and populationDescribe what the control should achieve, who operates it, how often, and every system or transaction it covers. Document exclusions and why they are justified rather than silently shrinking the sample.
- Retain source evidenceKeep a dated record of the request, approval, execution, and result where applicable. Link reused evidence to each requirement while preserving differences in scope, testing method, and reporting period.
- Review gaps explicitlySeparate missing evidence, known control failures, accepted exceptions, and untested areas. Assign corrective action and a retest. An audit outcome or completed questionnaire does not guarantee future security.
What to measure
Define the population and decision before choosing a target. The same percentage can conceal missing assets, untested cases, or evidence outside the review period. Keep the underlying counts so someone else can reproduce the result.
| Measure | Calculation or definition | How to use it |
|---|---|---|
| Population coverage | Control items with evidence / total applicable population | Record exclusions and sampling limits alongside the percentage. |
| Evidence freshness | Evidence within the required review period / evidence reviewed | Use the actual obligation or control cadence for the cutoff. |
| Verified remediation | Failed controls retested successfully / failed controls reported fixed | Keep evidence gaps distinct from confirmed control failures. |
Worked example: read the denominator
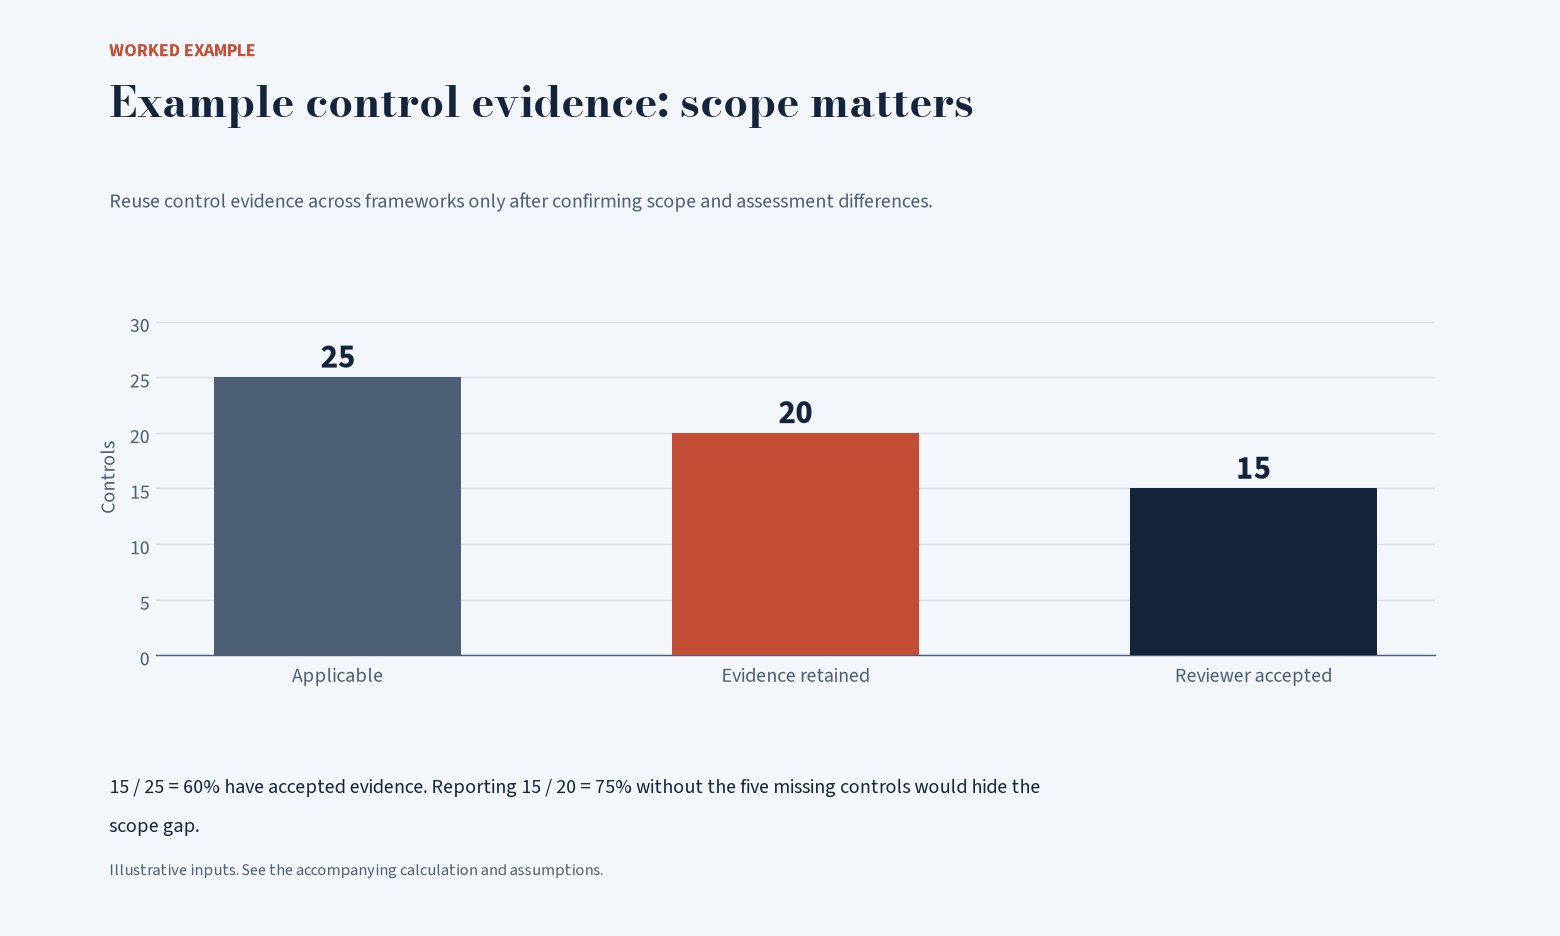
Worked example. Figures are illustrative.
| Observation | Controls |
|---|---|
| Applicable | 25 |
| Evidence retained | 20 |
| Reviewer accepted | 15 |
Interpretation
15 / 25 = 60% have accepted evidence. Reporting 15 / 20 = 75% without the five missing controls would hide the scope gap.
Keep all applicable controls in the denominator, including those with missing evidence.
Use your own operating data and record the reporting period, scope, exclusions, and accountable owner.
Documentation and acceptance criteria
The deliverable: A control crosswalk with common evidence and explicit framework-specific gaps.
Keep the scope and source records alongside the operator, date, expected outcome, actual result, and approving owner. Record what was not tested and any remaining exception. Have a reviewer reproduce one material conclusion from the original evidence before marking the work complete.
Next step: Start with the exercise above, assign an owner, and agree on the acceptance criteria. Review the results before expanding the work.
References
- NIST Cybersecurity Framework — Use outcomes and organizational context to organize the risk discussion; a framework mapping is not a control test.
- NIST SP 800-218: Secure Software Development Framework — Organize secure development, software protection, vulnerability response, and supplier communication.
Keep reading.
The End-of-Year IT Checklist Nobody Enjoys but Everyone Needs
Finish the year with verified service ownership and recovery readiness, rather than an unchecked task list. Review critical assets, account owners, contract renewals, certificate expiries, and the latest successful restore.
5 min read →What a Real Disaster Recovery Test Looks Like
Call a disaster recovery test successful only when the business service is usable and reconciled. Recover one critical service into an isolated environment without relying on the normal production administrator.
5 min read →
Refrigeration Alarms at 2 A.M.: Building a Response Plan That Works
Give a refrigeration alarm a response path that protects product and supports a sound disposition decision. Test sensor health, sustained alarm logic, acknowledgement, dispatch, and an alternative storage arrangement.
5 min read →